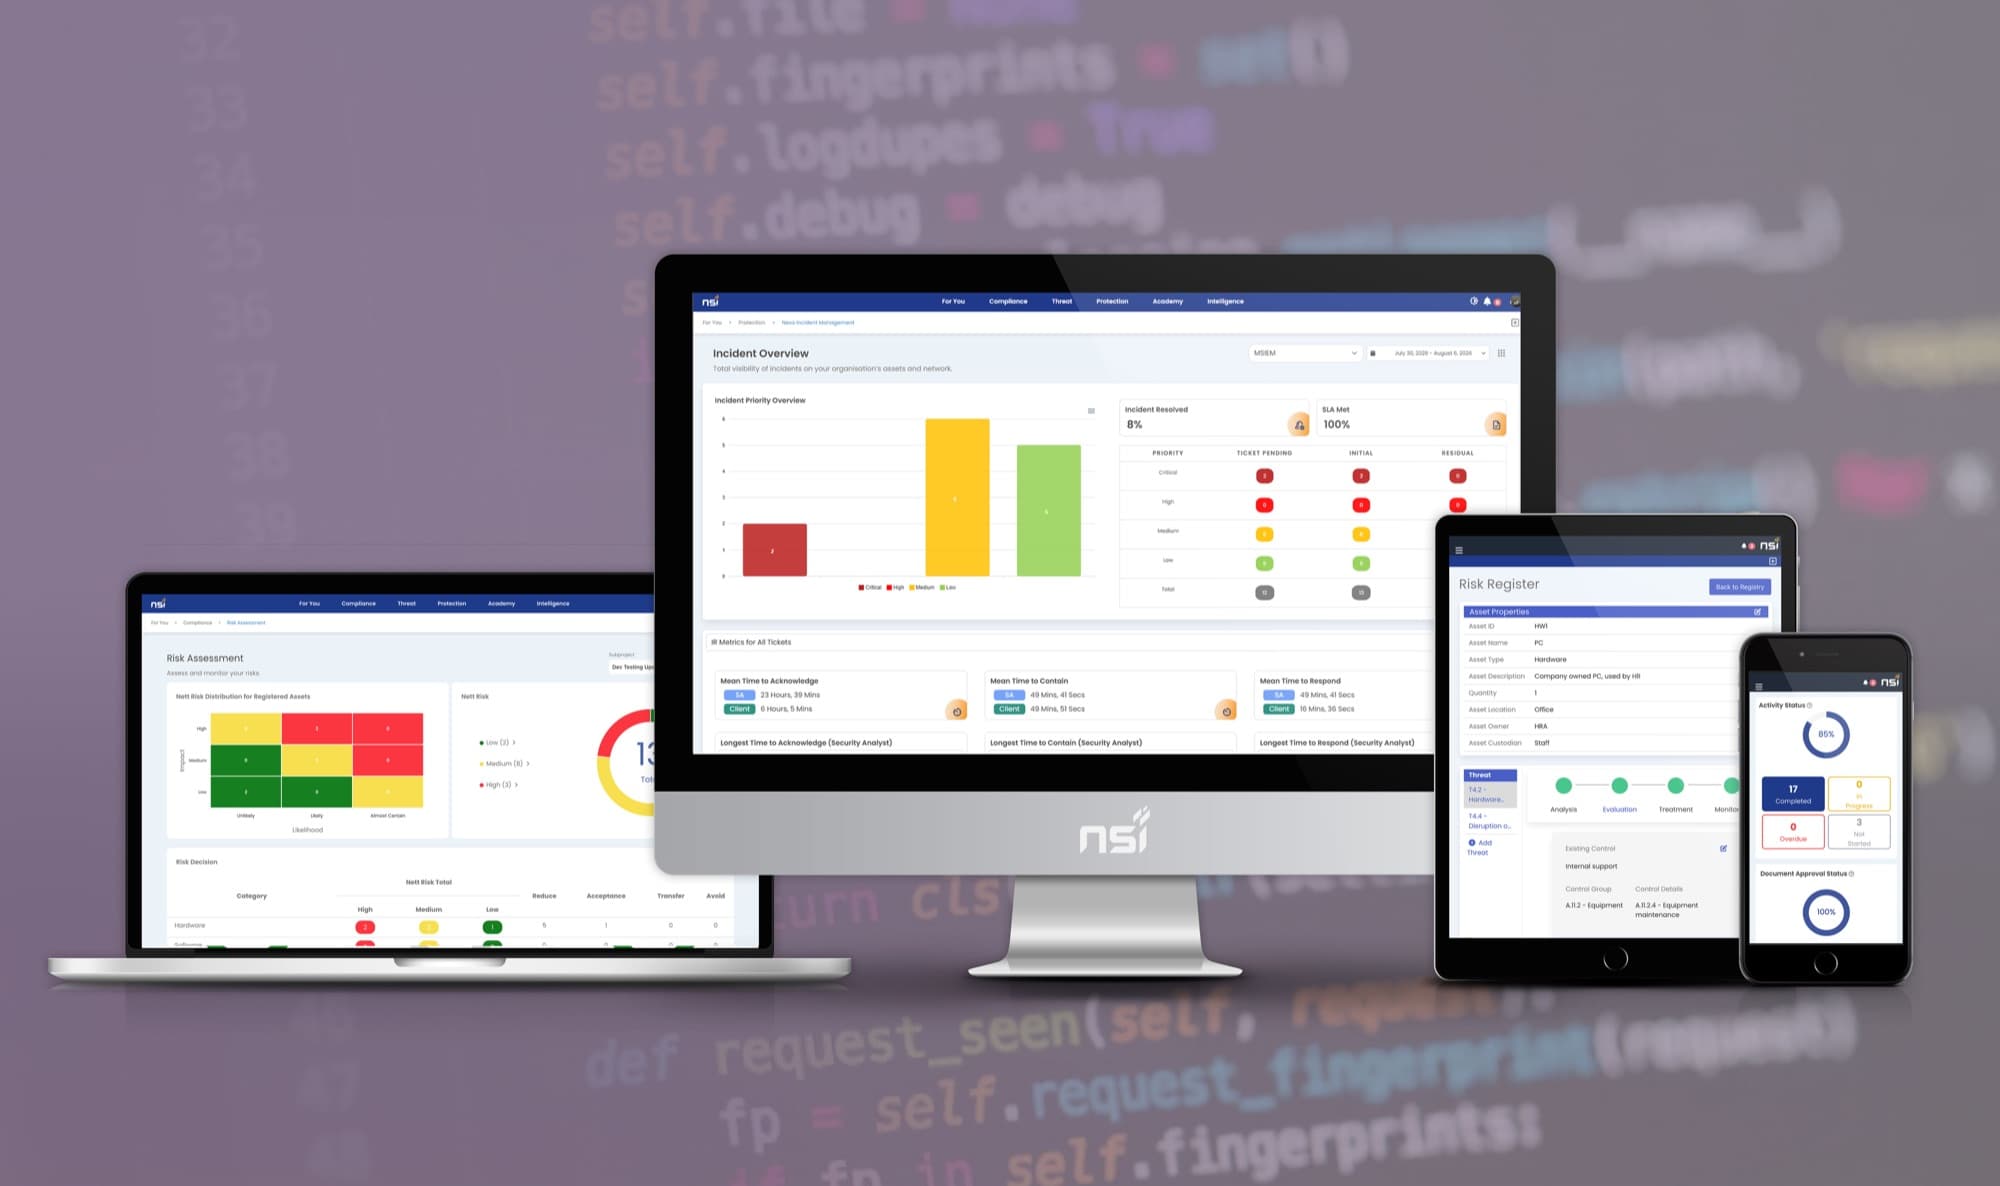
The platform behind the service.
NSI is the console our Global SOC works in, and the one you see the same view from. Compliance, threat visibility and protection in a single system.
Modules for every discipline
Whichever services you take, you see the modules that matter to the work you have bought, the same view our analysts work from.
Nexa Incident Management (NIM)
Structured incident management and SLA tracking across SIEM, MWSS, MDR and service requests, with our analysts and your team on the same ticket.
TI Hub: Threat Intelligence
Curated threat intelligence with an AI analysis layer over the feeds.
NSI Protection
Endpoint, WAF and DDoS controls with defacement and brand monitoring, managed from one console.
Security Assessment Platform (SPA) & VAPT
Scoping, testing and reporting for vulnerability assessment and penetration testing, tracked in one place.
Host Assessments (HAOS, HADB, HAND)
Configuration and hardening assessments across operating systems, databases and network devices.
Findings & Remediation Tracking
Every finding tracked from discovery to closure, with retest evidence held against it.
Compliance Module (ISMS ISO 27001)
Track implementation progress, generate SOPs and hold your evidence in one place. It is the module our own ISO 27001 certification runs on.
Risk Module (ISO 27005, CSA 854)
Risk assessment and treatment aligned to ISO 27005 and CSA 854.
Document, Records & Audit Facilitation
Controlled documents, records and audit trails ready for the external assessor.
Built to be the one system you keep.
One console
Compliance, threat visibility and protection integrated into a single platform, rather than a stack of disconnected tools.
Secure by design
The platform our own ISO/IEC 27001:2022 certification runs on, with the evidence trail built in.
Fast to deploy
Cloud-delivered modules that stand up in a fraction of the time a conventional roll-out takes.
Scales with you
Start with a single server or bring thousands of critical assets. Modules scale to the environment.
Managed or self-run
Every module can be run by your team or managed from our Global SOC.
Governed AI
AI capabilities operate under ISO/IEC 42001 (AIMS): automation first, analyst-in-the-loop.
Intelligence layered across the platform.
These components run in production today, governed under ISO/IEC 42001. Our analysts still make the call. NSI stops them doing the lookups by hand.
SIEM alert triaging
LiveML classification applied to Splunk alerts on arrival, so analysts start with the ones that matter.
Automated OSINT enrichment
LiveIndicators looked up across multiple intelligence sources automatically, instead of tab by tab.
TI Hub intelligence layer
LiveAnalysis over curated threat feeds, surfacing what is relevant to your environment rather than everything.
Threat module findings classification
LiveAssessment findings classified automatically to speed triage and prioritise remediation.
Risk Controls AI
LiveISO 27001 control suggestions drafted for review, so your team starts from a first pass rather than a blank page.
Ask for a walkthrough and we will show you the modules that map to the services you are considering. Email sales@nexagate.com.