Managed Security
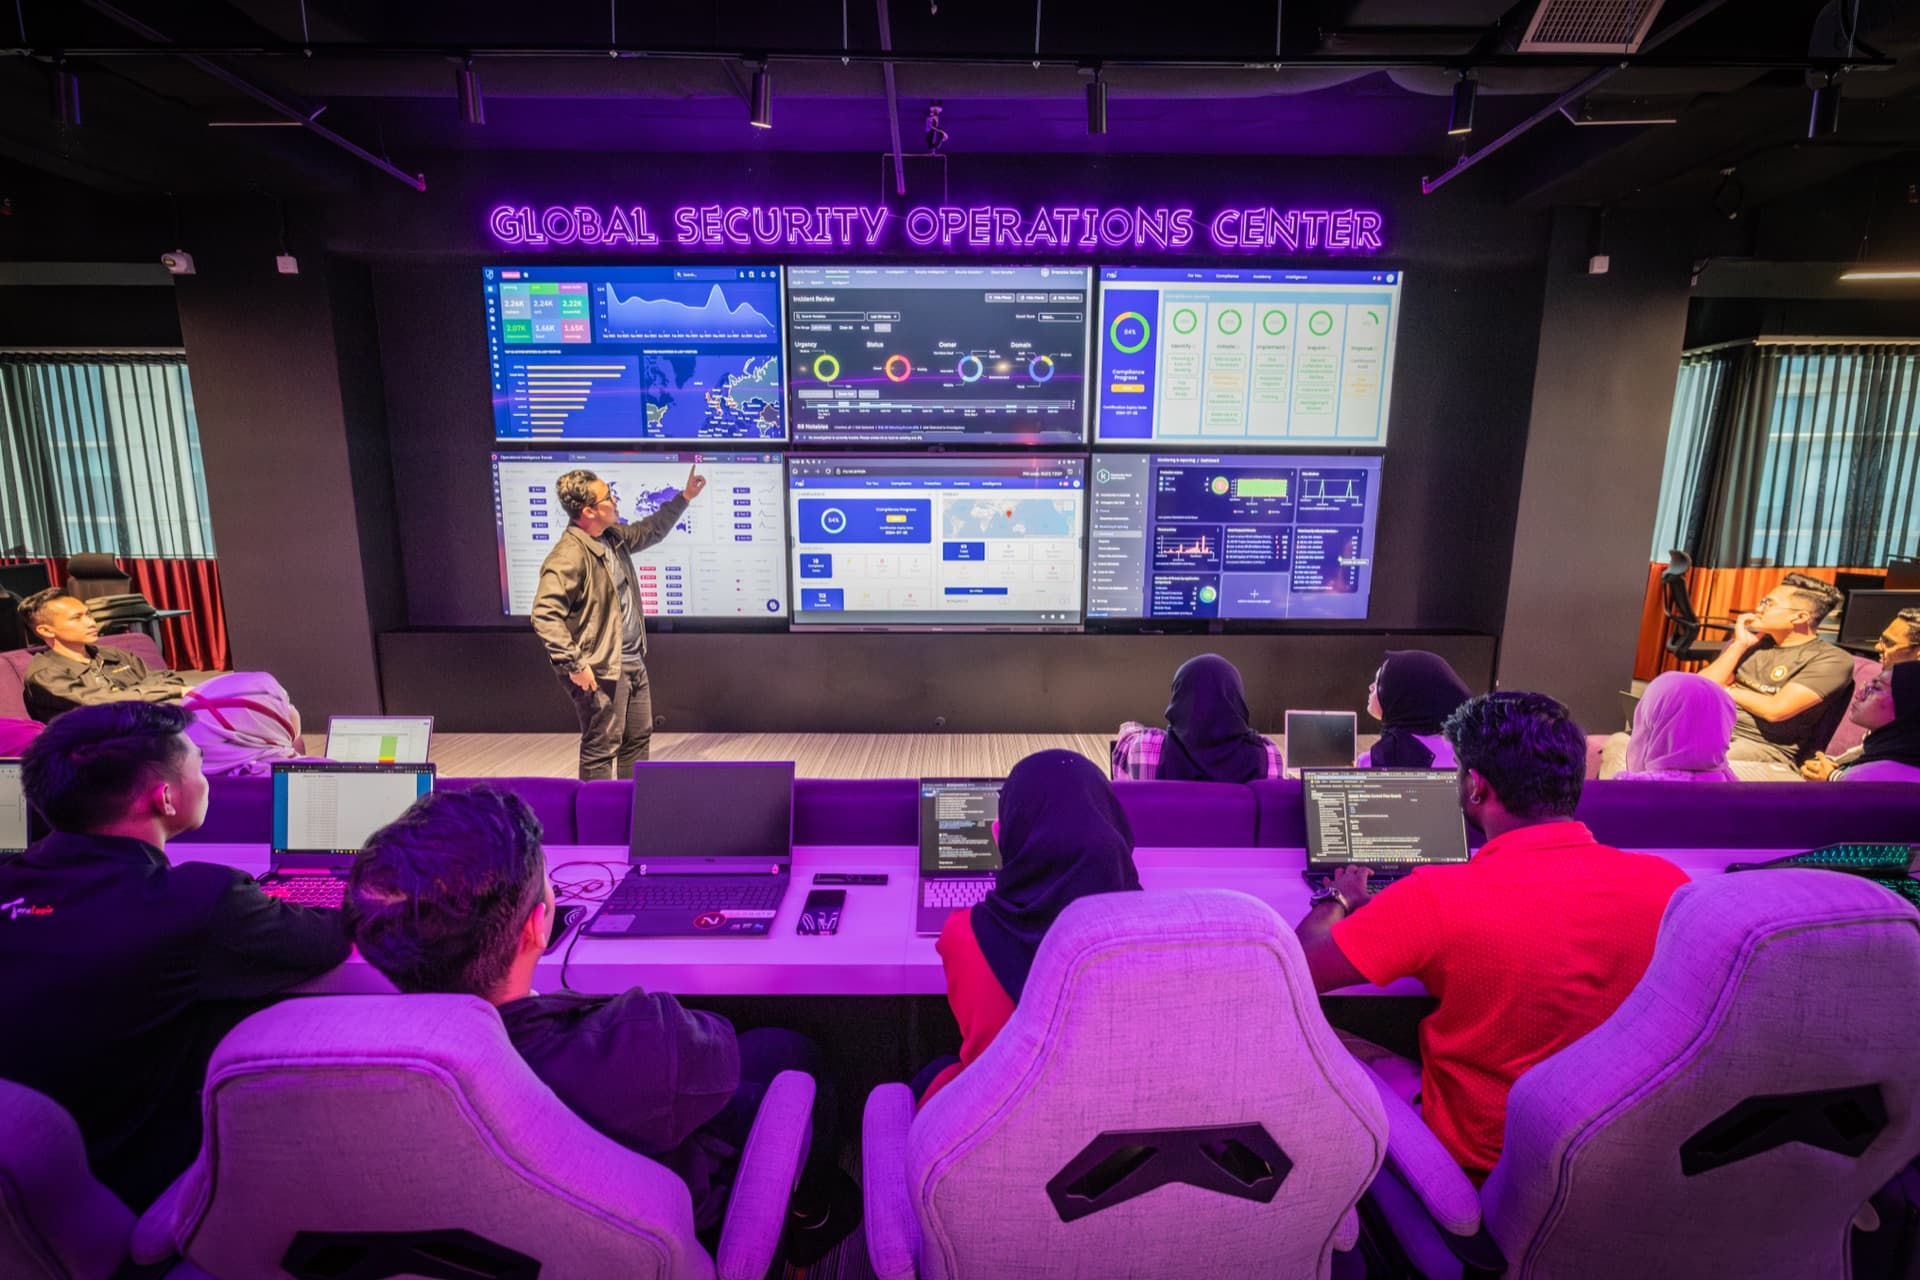
24/7 cybersecurity monitoring and incident response, delivered from the Nexagate Global SOC.
Most organisations can buy security tooling. Far fewer can staff it around the clock, tune it to their own environment and act on what it reports at three in the morning. That is the gap this pillar closes for financial services, government, telco, healthcare, utilities and manufacturing.
SOC-as-a-Service
SOC-as-a-Service gives your organisation complete security operations and monitoring on a subscription basis, with immediate access to our Global SOC. You get the experienced analysts, proven processes and leading detection technology of a mature security operations centre without the cost and delay of building one in-house.
Explore SOC-as-a-Service- 24/7 monitoring, triage and validation by experienced analysts
- Detection tuned to your environment during onboarding and refined over time
- Agreed escalation paths so genuine incidents reach the right people fast
- Actionable remediation guidance and events-based response playbooks
Everything in this pillar
Buy one, or run the whole set from a single contract and a single console.
SOC-as-a-Service
Subscription access to our Global SOC, analysts, processes and technology, monitoring you 24/7.
ResponseManaged Detection & Response
Detect and contain advanced threats across your endpoints with analyst-led detection and response.
CorrelationManaged SIEM & Incident Response
Splunk-backed SIEM and incident response for complete visibility from a single pane of glass.
CloudManaged Cloud Security
Continuous monitoring of your cloud infrastructure and applications across all major platforms.
EndpointManaged Endpoint Protection
Next-generation endpoint protection built on Kaspersky and CrowdStrike, managed by our analysts.
WebManaged Web Security
Imperva-backed WAF and bot control with security experts monitoring threats to your web applications.
AvailabilityManaged DDoS Protection
Always-on mitigation backed by a 10 Tbps global network against the largest and smartest attacks.
MigrationSplunk Cloud Migration
Zero-disruption migration from on-premises Splunk to Splunk Cloud, run by the team that runs your SOC.
Not sure where to start?
Most clients begin with SOC-as-a-Service and add capabilities as the environment grows.
Talk to a consultant →
One console, whichever services you take.
Every service in this pillar reports into NSI. You see the modules that matter to the work you have bought, the same view our analysts work from. Patented in Malaysia and Brunei.
See the full platform →Nexa Incident Management (NIM)
Structured incident management and SLA tracking across SIEM, MWSS, MDR and service requests, with our analysts and your team on the same ticket.
TI Hub: Threat Intelligence
Curated threat intelligence with an AI analysis layer over the feeds.
NSI Protection
Endpoint, WAF and DDoS controls with defacement and brand monitoring, managed from one console.
Intelligence layered into the service.
Automation first, intelligence on top. These components run in production today. Our analysts still make the call, but they stop doing the lookups by hand.
SIEM alert triaging
LiveML classification applied to Splunk alerts on arrival, so analysts start with the ones that matter.
Automated OSINT enrichment
LiveIndicators looked up across multiple intelligence sources automatically, instead of tab by tab.
TI Hub intelligence layer
LiveAnalysis over curated threat feeds, surfacing what is relevant to your environment rather than everything.
A consultant will scope the environment, size the service and come back with a quote, usually within one business day.